Blog

  • New Dyatlov Pass ‘Weapons Test’ Theory Reframes the Mystery as a Cold War Radiological Crime Scene

    New Dyatlov Pass ‘Weapons Test’ Theory Reframes the Mystery as a Cold War Radiological Crime Scene

    Key Takeaways

    • A fresh theory points to the Dyatlov Pass deaths as fallout from a Soviet weapons test involving thermobaric blasts and radiological exposure, challenging official avalanche narratives.
    • Key evidence includes unexplained radiation on clothing, blast-like injuries, and signs of a hasty cover-up, reframing the incident as a Cold War crime scene.
    • This perspective highlights ongoing risks from clandestine military programs, urging better preparedness against unseen hazards and state-controlled information flows.

    It’s late, the static on the shortwave crackles, and you’re out there scanning the horizons for patterns that don’t add up. We’ve all heard the Dyatlov Pass story—the nine hikers found dead in the Urals back in 1959, their tent slashed open from the inside, bodies scattered in the snow with injuries that scream something more than bad weather. But a new angle cuts through the fog: what if they wandered into a live Soviet weapons test? Not just any test, but one packing thermobaric punch and radiological traces. This isn’t about chasing ghosts; it’s about connecting dots to a systemic playbook that’s still in use today.

    The Night That Froze the Truth

    Picture this: February 1959, a group of experienced Soviet hikers sets up camp on a slope in the northern Ural Mountains. They were young, fit, led by Igor Dyatlov—engineers and students with a taste for the wild. What followed was chaos. Rescuers found their tent abandoned, ripped from within, footprints leading into the night. Bodies turned up over weeks: some with crushed skulls and chests, others with missing eyes or tongues, one with radiation on his clothes. Official word? Avalanche or katabatic winds. But those explanations have always felt thin, like a veil over something sharper.

    Enter this new lens from researchers piecing together declassified hints and forensic reexaminations. The hikers might have stumbled into a restricted zone where the Soviets were testing advanced munitions—thermobaric weapons that generate massive pressure waves without shrapnel, or perhaps early radiological devices. The Urals were a hotbed for secret ops back then, with nuclear facilities nearby. Imagine a blast wave ripping through the dark, slamming bodies without leaving craters, followed by a cleanup crew to stage the scene.

    Evidence That Radiates Suspicion

    Let’s sift through the traces. Autopsies showed injuries consistent with explosive overpressure: rib cages caved in like they’d been hit by an invisible hammer, no external wounds to match. One hiker’s jacket carried beta radiation levels off the chart—enough to suggest fallout from a dirty test. Photos from the site show a scorched tree line, as if a fireball had passed through. And the cover-up? Diaries and film rolls went missing, bodies were autopsied in secret, and witnesses reported orange spheres in the sky that night—maybe flares or test artifacts.

    Thermobaric weapons fit the puzzle: they create a vacuum effect, sucking oxygen and crushing with pressure. Mix in radiological elements from nearby labs like Mayak, infamous for its 1957 nuclear disaster, and you have a recipe for what unfolded. This isn’t wild speculation; it’s pattern recognition. The Soviets had form—testing nukes in remote spots, burying the collateral. Dyatlov becomes less a freak accident, more a footnote in Cold War black ops.

    From Historical Echo to Modern Warning

    What pulls this into our world isn’t just solving an old riddle. It’s the template it reveals: states running covert tests near civilian paths, then spinning narratives to contain the mess. Think about today’s drone swarms, hypersonic trials, or exotic energy weapons—often near borders or wildlands. We’ve seen leaks about unexplained contamination zones, hushed-up exposures. This Dyatlov reframing spotlights the risks: blast waves that leave no trace, radiation that lingers unseen.

    It ties straight to staying sharp. On the info side, it’s about dodging narrative traps—using secure channels to share findings, archiving data beyond state reach. Physically, it’s prepping for the unseen: Geiger counters in your kit, off-grid radios for when grids falter, evasion plans if you’re near test ranges. We’ve got patterns repeating; recognizing them could be the edge we need.

    Frequently Asked Questions

    It zeroes in on thermobaric blasts and radiation as the kill mechanism, backed by injury patterns and site anomalies, turning a vague mystery into a pointed critique of state secrecy—not just wind orYetis.

    Traces on clothing suggest exposure from a nearby test or fallout, linking to Soviet nuclear sites; it’s the thread that pulls the cover-up narrative apart, hinting at a radiological crime scene.

    It’s a blueprint for how governments handle clandestine tests and collateral—lessons in spotting info suppression and prepping for hazards like overpressure or contamination in today’s black-budget world.

    Build redundancy: secure your data with encrypted archives, kit up with environmental monitors, and map evasion routes near potential test zones—patterns like Dyatlov show the risks are real and repeating.
  • Azure’s 15.7 Tbps DDoS Attack: How the Aisuru Botnet Exposed Our Cloud Dependency

    Azure’s 15.7 Tbps DDoS Attack: How the Aisuru Botnet Exposed Our Cloud Dependency

    Key Takeaways

    • The Aisuru botnet unleashed a 15.72 Tbps DDoS attack on Microsoft’s Azure, revealing how centralized cloud systems can become single points of failure in our digital world.
    • This incident underscores the hidden risks of botnets, quietly amassing power from compromised devices, much like unseen forces building in the shadows before striking.
    • Building personal resilience—through backups, multi-provider strategies, and vigilant security—can shield against cascading outages that disrupt everything from banking to communications.

    The Strike from the Shadows

    It’s late at night, and you’re scrolling through the feeds, piecing together patterns that the mainstream glosses over. That’s when a report like this lands: Microsoft confirming a staggering 15.72 terabits per second DDoS attack on their Azure cloud platform, courtesy of the Aisuru botnet. This isn’t just a blip in the system; it’s a wake-up call about how deeply we’ve woven our lives into these vast, centralized networks. One massive surge, and the threads start unraveling.

    The details come from BeforeCrypt’s News Week summary for November 17th to 23rd, 2025—a quiet corner of the web where these stories surface without the polish of corporate spin. Azure, powering everything from enterprise data centers to everyday apps, took the hit head-on. The scale? Unprecedented in its raw power, flooding servers with junk traffic to overwhelm and deny service. It’s the kind of event that makes you question: who’s really in control when a botnet can muster that kind of force?

    Decoding the Aisuru Botnet

    Aisuru—named perhaps after some elusive concept, like a ghost in the machine—operates by hijacking everyday devices. Think routers, smart cams, even IoT gadgets left unpatched and vulnerable. These aren’t flashy hacks; they’re slow infiltrations, building an army in plain sight. Once assembled, they coordinate to unleash torrents of data, targeting weak spots in cloud infrastructure.

    What sets this apart is the sophistication. It’s not random chaos; it’s a test of resilience, exposing how a single platform’s downtime could cascade into broader disruptions. Government sites, financial systems, even critical services rely on Azure or similar clouds. If one falls, others feel the ripple. We’ve seen echoes of this in past events, but 15.72 Tbps pushes it into new territory, hinting at capabilities that could be redeployed anywhere.

    Cloud Dependency: The Hidden Web

    Step back, and you see the bigger picture. Our world runs on these cloud giants—Microsoft, Amazon, Google—concentrating power in fewer hands. It’s efficient, sure, but it’s also a vulnerability. Black-budget programs thrive on opacity, and here we have a digital parallel: invisible concentrations of infrastructure that, when targeted, could paralyze sectors like healthcare or transportation. The Aisuru attack isn’t isolated; it’s a symptom of how botnets can be weaponized quietly, perhaps by state actors or rogue groups probing for weaknesses.

    Remember those unexplained aerial phenomena we track? They often involve tech that’s steps ahead, hidden from view. This cyber realm feels similar—unseen networks amassing, striking without warning. The difference? We can prepare for this one.

    Fortifying Your Perimeter

    So, what do we do? Start with the basics: secure your devices to avoid feeding the botnet beast. Patch software, enable two-factor authentication, use VPNs to mask your traffic. Go further—diversify. Don’t put all your data in one cloud basket; mix in local backups and multi-provider setups. For critical stuff like email or payments, have offline contingencies ready. Monitor your network for odd patterns; tools like traffic analyzers can spot anomalies early.

    This isn’t paranoia; it’s pattern recognition. We’ve seen how quickly things can shift, from blackouts to data breaches. By hardening your setup, you’re not just protecting yourself—you’re weakening the web that botnets like Aisuru rely on.

    Frequently Asked Questions

    Aisuru is a network of compromised devices, from routers to IoT gadgets, coordinated to flood targets with traffic. It hit Azure with 15.72 Tbps, testing the platform’s defenses and exposing gaps in cloud security.

    It highlights our reliance on centralized clouds. If Azure stumbles, it could disrupt banking, work tools, or communications—pushing us to build redundancies and avoid single-point failures.

    Keep devices updated, use strong passwords with 2FA, run anti-malware scans, and monitor traffic. Diversify your services to minimize risks from any one provider going down.

    Absolutely—botnets mirror the stealth of black-budget ops or aerial anomalies, building power unseen. Recognizing these patterns helps us prepare for disruptions, digital or otherwise.

  • When the Simulation Glitches: A Cascade of ‘Impossible’ Disasters and What It Means for Your Grid Survival

    When the Simulation Glitches: A Cascade of ‘Impossible’ Disasters and What It Means for Your Grid Survival

    Key Takeaways

    • A single day—November 28, 2025—saw an unprecedented cluster of natural disasters and sky anomalies, framed as a “simulation glitch,” highlighting vulnerabilities in our power grids and infrastructure.
    • These cascading events underscore the fragility of centralized systems, from weather extremes to geological shifts, urging a shift toward personal resilience in grid-down scenarios.
    • Actionable steps include building backup power, securing off-grid communications, and hardening data practices to maintain situational awareness amid disruptions.

    The Day the Code Cracked

    Picture this: you’re staring at the feeds, the ones that bypass the official channels, and there it is—a perfect storm of anomalies all hitting on the same date, November 28, 2025. Earthquakes rattling foundations in unexpected places, volcanic plumes choking the skies, freak storms tearing through grids, and those unexplained lights dancing overhead like faulty pixels in the render. It’s the kind of pattern that makes you sit up in the dim glow of your screen, connecting dots that the mainstream dismisses as coincidence.

    This isn’t some abstract theory pulled from late-night forums. It’s grounded in reports compiled by outlets like Strange Sounds, where the author frames it as the simulation glitching—beautifully, they say, but with an edge that cuts deep into our reality. We’re talking real-time breakdowns: power outages cascading from flooded substations, supply chains snapping under geological strain, and communication blackouts where the sky itself seems to interfere. If this is a simulation, it’s one that’s starting to show its seams, and those seams run right through the systems we rely on every day.

    Patterns in the Chaos: Why It Matters for the Grid

    Let’s break it down without the fluff. When multiple stressors hit at once—say, a solar flare messing with satellites while earthquakes disrupt underground cables—it’s not just bad luck. It’s a cascade that exposes how thin the veil is between stability and blackout. Power grids, those vast networks of wires and transformers, aren’t built for this level of overlap. One glitch leads to another: a storm knocks out primary lines, backup generators fail under ash from a distant eruption, and suddenly you’re in the dark, cut off from water pumps, fuel stations, and the digital threads that hold society together.

    I’ve tracked these patterns for years, from black-budget whispers to eyewitness accounts of aerial oddities. This cluster fits the mold of simulation theory, where our perceived world is a complex program hitting its limits. But forget the philosophy; the real hook is the risk. Infrastructure in critical sectors—transport, energy, comms—crumbles fast when anomalies stack up. And if you’re following these on social feeds or anomaly-tracking apps, remember: those platforms can glitch too, leaving you blind unless you’ve prepped your own setup.

    Fortifying Against the Glitch: Your Resilience Playbook

    Here’s where it gets practical. If the simulation’s fraying, don’t wait for the reset. Start with power: invest in solar backups or generators that can run independent of the grid. Stock water and food for at least a couple of weeks—think non-perishables, filtration systems, things that don’t need electricity to prepare. Communications? Go off-grid with ham radios or mesh networks that don’t rely on cell towers.

    On the data side, harden your edge. Use VPNs to mask your tracking of these events, switch to secure messengers for sharing intel with your circle, and keep offline copies of maps, survival guides, and anomaly databases. Centralized warnings might fail when the cascade hits, so build your own radar. This isn’t paranoia; it’s pattern recognition. We’ve seen it before in isolated incidents—now imagine them synced up. Your move is to decouple from the fragile center and stand firm on your own ground.

    Frequently Asked Questions

    Reports point to a mix: major quakes in stable zones, volcanic activity spiking, extreme weather blackouts, and unexplained aerial lights—all syncing up in a way that defies random chance, like code errors compounding.

    When disasters cluster, they overload grids—storms flood lines, quakes snap cables, anomalies disrupt signals. It’s a chain reaction that leaves infrastructure reeling, far beyond what single events cause.

    Secure backup power, like solar kits or fueled generators, and pair it with water storage. From there, layer in secure comms to track patterns without relying on failing networks.

    If you’re pulling intel from underground sources, disruptions can cut access. VPNs and offline archives ensure you stay informed, even when the digital grid glitches out.

  • “I Was Being Trafficked to Canada”: Kidnapped Woman Fights Back on Pennsylvania Turnpike

    “I Was Being Trafficked to Canada”: Kidnapped Woman Fights Back on Pennsylvania Turnpike

    Key Takeaways

    • A kidnapped woman escaped sex trafficking en route to Canada by stabbing her captor on the Pennsylvania Turnpike, exposing how traffickers exploit interstate highways for covert victim transport.
    • This case reveals systemic risks in long-distance travel, including drugging and restraints, underscoring patterns in organized networks that use borders and infrastructure to evade detection.
    • Strengthening personal preparedness—through situational awareness, self-defense tactics, and digital security measures—can empower individuals to disrupt these hidden pipelines and protect against targeting.

    A Desperate Break on the Open Road

    Picture the Pennsylvania Turnpike at dusk: endless lanes carving through hills, trucks blending into the flow. That’s where one woman’s nightmare shifted. Kidnapped from Reno, she was drugged, zip-tied, and hauled east in a GMC Sierra, bound for Canada’s sex trade circuits. But she fought back—grabbing a knife, stabbing the driver, and halting the truck. State police pieced it together: an organized run, using America’s highways as silent conduits for human cargo. It’s the kind of story that lingers, not just for the escape, but for what it uncovers about the shadows moving alongside us.

    These aren’t random abductions; they’re calculated. The victim reported being targeted, subdued with drugs to dull resistance, and restrained for the long haul. The route? From Nevada across states, aiming for the northern border where enforcement thins. It’s a tactic I’ve tracked in similar accounts—traffickers treating interstates like veins, pumping victims toward international handoffs. This one broke the pattern, but it reminds us: these operations hide in plain sight, relying on speed and the anonymity of the road.

    Unmasking the Systemic Web: Highways as Trafficking Arteries

    In my years digging into overlooked connections—from anomalous sightings to covert programs—I’ve learned patterns repeat. Here, it’s the infrastructure itself: the Pennsylvania Turnpike, a major corridor, becomes a vulnerability. Traffickers scout routes that minimize stops, timing crossings to slip past patrols. Borders like the U.S.-Canada line aren’t barriers; they’re gateways for those who know the gaps. Add in drugs for control and zip ties for restraint, and you’ve got a system designed to move people undetected, often starting with lures in rideshares or vulnerable spots.

    What makes this urgent? It’s current, it’s real, and it ties into broader pipelines. Reports like this one highlight how routine travel—long drives, shared rides—can turn into traps. The Turnpike incident isn’t isolated; it’s a node in a network where victims are funneled north, away from origin points. Spotting these threads means looking beyond the surface: who owns the vehicles, what digital trails lead to recruiters, and how borders facilitate the endgame.

    Building Your Defenses: Survival and Security Tactics

    If you’re tuned into the unexplained, you already question the official narrative. Apply that to personal risk: this story calls for action. On the physical side, hone situational awareness—watch for red flags in vehicles, like unexpected route changes or companion behaviors. Discreet self-defense? Think pepper spray, a tactical pen, or yes, a knife if legal—tools that fit in a pocket but deliver in a pinch. Under restraint? Practice mental escape planning: identify weak points like loose ties or driver distractions, and signal for help subtly, maybe by forcing a stop or alerting passersby.

    Don’t overlook the data layer. Traffickers hunt online; counter it with hardened habits—use secure apps for real-time location sharing with trusted contacts, document vehicle plates and descriptions before any ride, and minimize your digital footprint to starve predators of targeting info. Pre-plan emergency signals, like coded texts or apps that trigger alerts. This isn’t about living in fear; it’s about reclaiming control, turning potential vulnerabilities into strengths. The Turnpike survivor did it—her story shows the way forward.

    Frequently Asked Questions

    A woman from Reno was kidnapped, drugged, and zip-tied in a GMC Sierra headed to Canada for sex trafficking; she escaped by stabbing the driver, prompting a police response and arrest.

    Interstates like the Turnpike serve as fast, low-visibility routes for moving victims across states and borders, allowing traffickers to blend in and evade routine checks.

    Build awareness of surroundings, carry discreet defenses like spray or knives, practice restraint escapes, and use pre-planned signals to alert others during travel.

    Predators use online data to target victims; secure location-sharing, documenting identifiers, and reducing digital exposure limit their access and enhance real-time protection.

    Absolutely—it’s part of systemic pipelines exploiting U.S. infrastructure and Canadian borders for quick, covert victim transport, connecting to ongoing organized networks.

  • Pentagon Quietly Raises America’s Cyber DEFCON: CMMC Enforcement Exposes Defense Supply Chain Weak Links

    Pentagon Quietly Raises America’s Cyber DEFCON: CMMC Enforcement Exposes Defense Supply Chain Weak Links

    Key Takeaways

    • The Pentagon’s enforcement of CMMC 2.0 via a new DFARS rule in 2025 elevates America’s cyber defense posture, mandating stricter cybersecurity for all defense contractors amid widespread noncompliance.
    • This shift exposes systemic vulnerabilities in the defense supply chain, particularly among smaller suppliers with outdated systems, potentially disrupting operations and revealing hidden weaknesses in black-budget programs.
    • Individuals and small businesses should mirror this heightened alert by adopting zero-trust practices, VPNs, and offline backups to safeguard against cascading cyber threats.

    Pentagon Quietly Raises America’s Cyber DEFCON: CMMC Enforcement Exposes Defense Supply Chain Weak Links

    Picture this: It’s the dead of night, and somewhere in the shadowed halls of the Pentagon, a switch flips. Not with fanfare or press releases, but through a quiet rule change in the Federal Register. On November 10, 2025, the Department of Defense rolled out enforcement of the Cybersecurity Maturity Model Certification (CMMC) 2.0, baked into DFARS clauses like 252.204-7021 and 7025. This isn’t just paperwork—it’s a de facto raise in our national cyber DEFCON level, forcing every contractor in the defense industrial base to prove their digital fortifications or get locked out of the game.

    We’ve tracked black-budget programs and unexplained aerial phenomena for years, piecing together patterns that the mainstream overlooks. But this move connects dots in a different shadow: the underbelly of America’s defense supply chain. Think about it—the same networks handling classified UAV tech or experimental propulsion systems are now under scrutiny. The Pentagon admits many contractors aren’t ready. Smaller suppliers, often the unsung links in the chain, run on exposed legacy systems, ripe for infiltration. One weak node, and the whole structure tremors.

    This enforcement isn’t coming out of nowhere. It’s a response to patterns we’ve seen building: state-sponsored hacks probing defense perimeters, supply-chain attacks that echo the SolarWinds breach. CMMC 2.0 demands zero-trust architectures, encrypted communications, rigorous access controls, and ironclad incident response plans. Offline backups? Mandatory. It’s like they’re bracing for an invisible war, one where the battlefield is code and the casualties are data breaches that could unmask sensitive operations.

    The Systemic Cracks in the Armor

    Let’s zoom in on the vulnerabilities. The defense industrial base isn’t a monolith—it’s a web of primes, subs, and tiny vendors. Many of these smaller players lack the resources for full compliance. Audits show gaps in basic hardening: unpatched software, weak multifactor authentication, networks wide open to the internet. The Pentagon’s own assessments reveal that noncompliance could sideline thousands of contracts, creating bottlenecks in everything from munitions to advanced sensors.

    For those of us watching black-budget edges, this raises flags. What happens when a noncompliant supplier tied to a classified program gets cut off? Disruptions could ripple into anomalous tech development—those unexplained sightings might tie back to interrupted R&D. And if adversaries exploit these weak links, we’re talking potential leaks of data that could rewrite what we know about hidden aerial programs.

    Patterns like this don’t emerge in isolation. We’ve seen similar escalations before: post-9/11 security ramps, the pivot to cyber after Stuxnet. This CMMC push feels like preparation for something bigger—a recognition that our cyber posture has been too lax, too trusting, in an era of persistent threats.

    Upgrading Your Own Cyber DEFCON

    If the Pentagon is locking down its ecosystem, it’s a signal for the rest of us. You, tracking these threads from your setup, know better than to ignore it. Start with the basics: Enable zero-trust on your devices—verify every access, every time. Use a solid VPN to mask your traffic, especially when digging into sensitive archives. Manage passwords with encrypted vaults, and rotate keys regularly.

    Harden your gear: Segment critical systems from the open web, keep offline backups of key data. Prepare for supply-chain fallout—if defense vendors falter, it could spike costs or delays in civilian tech. This isn’t paranoia; it’s pattern recognition. The same forces probing defense networks won’t stop at the gates.

    We’re in this together, peering into the unexplained. This cyber shift is another layer, another connection. Stay vigilant— the truth often hides in the code.

    Frequently Asked Questions

    CMMC 2.0 is the Pentagon’s framework for certifying cybersecurity maturity in defense contractors. Enforcement via DFARS rules in 2025 stems from mounting threats—it’s a quiet escalation to plug holes in the supply chain before they become entry points for bigger intrusions.

    Weak links in the defense supply chain could expose classified tech, including anomalous aerial projects. Noncompliance might disrupt R&D, creating patterns that echo in unexplained sightings or leaked data—we’re watching those connections closely.

    Mirror the Pentagon’s playbook: Adopt zero-trust verification, use VPNs for secure browsing, encrypt your data, and maintain offline backups. It’s about hardening your own perimeter against the same shadows targeting defense networks.

    Absolutely—many smaller contractors aren’t ready, which could lead to contract cutoffs and supply-chain snarls. Keep an eye on how this shakes out; it might reveal deeper vulnerabilities in hidden programs.

  • CIA Séance with Sybil Leek: The Evidence They Hid?

    CIA Séance with Sybil Leek: The Evidence They Hid?

    Key Takeaways

    • Community accounts claim a September 1972 séance attended by CIA and military intelligence officers with Sybil Leek, during which a voice calling itself ‘Caxuulikom’ allegedly said ‘Earth is a farm. You are the cattle.’
    • There is no publicly available contemporaneous transcript, official memo, or mainstream-press record that independently corroborates the specific 1972 séance or the ‘Caxuulikom’ utterance.
    • Government records confirm MK-era programs (MKULTRA, MKOFTEN/OFTEN) explored behavioral, pharmacological and some parapsychological topics in the late 1960s–early 1970s; however, the specific linkage between those programs and the Leek séance is unproven.

    A Candlelit Room, Men in Suits

    Picture a dim room in 1972, flickering candlelight casting long shadows on the walls. Sybil Leek, the English witch and author born in 1917, sits at the center, surrounded by men in sharp suits—said to be from CIA and military intelligence. According to community lore, a voice emerges during the séance, identifying as ‘Caxuulikom’ and declaring, ‘Earth is a farm. You are the cattle.’ These details come from anecdotal reports, not confirmed documents, painting a scene thick with Cold War tension and occult curiosity.

    What Witnesses and Analysts Report

    In UFO and paranormal circles, the story spreads through fringe writers, blogs, podcasts, and forums. They describe the 1972 séance with Leek and intelligence officers, highlighting the ‘Caxuulikom’ entity and its chilling farm metaphor. Many connect this to the supposed ‘Collins Elite’ think tank, framing some UAP as demonic rather than extraterrestrial. The ‘Earth-as-farm’ idea echoes older motifs from Charles Fort and New Age thought, which might explain its recurrence. These claims rely on secondary sources and community testimony—no original eyewitness statements or transcripts have surfaced publicly.

    Timelines, Tracks, and Hard Data

    Sybil Leek lived from February 22, 1917, to October 26, 1982, known for her occult writings. Jack Parsons, the rocket engineer and Thelema practitioner, was born October 2, 1914, and died June 17, 1952—his dual life in science and the occult is well-documented in institutional records. Project MKOFTEN appears in declassified DoD and CIA files as a program from the late 1960s to early 1970s, focusing on behavioral and toxicological experiments. Yet searches turn up no mainstream articles, memos, or archives confirming the 1972 séance, the ‘Caxuulikom’ quote, or a formal ‘Collins Elite.’

    Claimed Item Documentary Support
    Séance date (September 1972) Secondary sources and community claims; no primary documents
    Participants (CIA/military intelligence, Sybil Leek) Anecdotal reports; no authenticated records
    ‘Caxuulikom’ quote Community testimony; no transcripts or memos
    Collins Elite existence Oral claims and secondary synthesis; no archival proof

    Official Story vs. What the Data Suggests

    Declassified files from the CIA and DoD confirm MKULTRA-era programs delved into pharmacology, behavior mods, and parapsychology, though many were destroyed or redacted. JPL and Caltech records note Parsons’ rocketry work alongside his occult pursuits, without endorsing supernatural ties to UAP. No official documents back the 1972 séance details or ‘Collins Elite.’ Community views split: some see demonic forces in UAP, others view the tale as folklore or misplaced anecdote. Records prove government interest in the fringes, but speculation fills the gaps where proof ends.

    What It All Might Mean

    The firmest threads include Leek’s public occult role, proven U.S. experiments in parapsychology via MKOFTEN, and figures like Parsons blending science with the esoteric. Major holes persist—no primary docs for the séance or ‘Collins Elite.’ What if private papers or classified files hold memos from that era? Did MKOFTEN assign officers to occult meetings? FOIA requests targeting CIA, DoD offices, NARA, and private archives could uncover more—phrasing them for ‘parapsychological consultations 1970-1975’ might yield results. Readers, if you’ve got leads, let’s chase them.

    Frequently Asked Questions

    Community accounts describe a September 1972 séance attended by intelligence officers where ‘Caxuulikom’ spoke. No public transcripts or official memos confirm it, leaving the event in the realm of anecdotal reports.

    The quote circulates through fringe sources and forums, often linked to theories of demonic UAP. It lacks documentary backing like transcripts, but echoes older cultural motifs from writers like Charles Fort.

    Claims of this think tank come from oral histories and secondary accounts, tying it to occult UAP views. Archival searches find no evidence of its official existence or funding.

    Declassified records show MKULTRA and MKOFTEN explored parapsychology in the late 1960s–early 1970s. No direct links to the Leek séance appear, but the programs confirm interest in fringe topics.

    Targeted FOIA requests to CIA, DoD, and NARA for parapsychological records from 1970-1975 could help. Interviews with survivors or checks of private archives might reveal memos or notes.

  • Venezuelan Narco-Plane Shootdown: Facts & All Claims

    Venezuelan Narco-Plane Shootdown: Facts & All Claims

    Key takeaways

    • Venezuelan Armed Forces (FANB) reported intercepting and neutralizing an unauthorized light aircraft that landed on a clandestine dirt strip in Rómulo Gallegos Municipality, Apure state.
    • FANB released videos dated Oct 28–30, 2025, showing a damaged small twin‑engine aircraft with a ground blaze; the plane reportedly had its transponder off and was declared hostile.
    • Several regional outlets and aviation hobbyists identified the type as a Cessna 310 and cited registration XB-RED; claims that two Colombian nationals were killed remain unverified.

    Summary

    Available open sources align on FANB messaging and posted footage, but critical evidentiary gaps persist: no public ADS-B or radar tracks have been produced, casualty and identity confirmations are lacking, and there are no independent forensic details about the weapon or method used to neutralize the aircraft. The incident fits a pattern of multiple FANB interdictions of unauthorized small aircraft in 2025, raising concerns about civil aviation safety and cross-border tensions.

    Recommended verification steps

    • Obtain original FANB video files and timestamps for metadata analysis.
    • Search ADS-B and primary radar archives for Oct 28–30, 2025, and consult aggregators such as ADS-B Exchange.
    • Contact Colombian authorities for casualty and identity confirmation.
    • Request details from Venezuelan authorities on the engagement protocol and means of neutralization.
    • Use reverse-image searches and fact-checker networks to weed out manipulated or recycled footage.

    Until independent data emerges, the official narrative should be treated as partially corroborated: video and local reports support that an aircraft was disabled, but aircraft identity, origin, casualties, and the exact engagement method remain unconfirmed.

  • Infrasound and Hauntings: The Frequency Ghost Myth

    Infrasound and Hauntings: The Frequency Ghost Myth

    Key Takeaways from the Frequency Files

    • Laboratory and experimental work has repeatedly flagged a cluster of low frequencies (near ~18–19 Hz) that correlate with reports of ‘haunting’ sensations in some settings (Tandy & Lawrence, 1998; Goldsmiths Haunt project used 18.9 Hz and 22.3 Hz).
    • Institutional reviews (WHO 2018; multiple systematic reviews) find limited, inconsistent evidence that sub-audible infrasound at typical environmental levels causes unique physiological harm — strongest links are to annoyance, sleep disruption and stress pathways rather than a specific infrasound pathology.
    • Open, consequential unknowns remain: what mechanism would let inaudible infrasound reliably produce apparitions in some people but not others, what real-world dose/configuration matters, and whether AI-generated music or production choices could be engineered at scale to steer mood or states without disclosure.

    A Low Hum in the Room

    It started in the lab, late one evening. Vic Tandy and his colleagues felt it before they understood it—a creeping cold that settled into the bones, shadows flickering at the edge of sight, and that unmistakable sense of something watching from the corners. The air smelled of stale coffee and metal dust, the kind of quiet where every creak echoes. Then, measurements revealed the culprit: an infrasound peak humming through the room, inaudible but insistent (Tandy & Lawrence, 1998).

    Across reports, the experiences share a pattern. People describe a sudden presence, like an unseen figure brushing past. Visual glitches appear in the periphery—fleeting shapes that vanish when you turn. Nausea hits, or a wave of unexplained sadness, paired with cold spots that chill the skin. It’s the uncanny quiet that amplifies it, where the absence of sound feels alive.

    Today, this ties into a broader cultural thread. Producers, meditators, and artists like Rick Rubin talk about sound as something spiritual, a force that shapes reality. It shifts how we listen, turning odd sensations into signs of deeper layers at work.

    What Witnesses and Analysts Report

    In haunted spots, the stories align. Witnesses speak of fear crashing in without warning, a felt presence that raises hairs on the neck, body tremors, cold patches, and quick visual distortions—all tied to a specific place. Tandy’s lab staff described exactly this before anyone checked the frequencies (Tandy & Lawrence, 1998).

    Near wind turbines, residents share their own accounts: persistent headaches, broken sleep, a pulsing inside the body, and dizzy spells. These reports fuel advocacy groups, even as debates rage over what’s really causing them.

    Sound-healing circles and New Age practitioners turn to Solfeggio frequencies—396 Hz for releasing fear, 417 Hz for change, 528 Hz for supposed DNA repair. They share these as tools for restoration, though mainstream biology hasn’t backed the claims.

    Figures like Rick Rubin frame sound production as a spiritual act, influencing mood and mind. This gives frequency ideas a cultural weight, making them feel like hidden knowledge worth exploring.

    Timelines, Tracks, and Hard Data

    The evidence builds from key studies and measurements. Here’s a quick reference:

    Frequency Source Claimed Effect Measured Amplitude (if available)
    ~18.9 Hz Tandy & Lawrence, ‘A Ghost in the Machine’ (Journal of the Society for Psychical Research, April 1998) Correlated with haunting sensations like sensed presence and visual anomalies Peak in investigated laboratory (not specified)
    18.9 Hz and 22.3 Hz Goldsmiths ‘Haunt’ experimental study (French et al.) Small increases in anomalous experiences under lab conditions Deliberately used components (amplitudes not detailed in summary)
    ≈18 Hz DTIC report (ADA030476) Eyeball resonant frequency, potentially linked to visual distortions Small amplification factor; complex coupling
    Sub-audible infrasound (general) WHO Environmental Noise Guidelines (2018) and literature reviews Limited evidence for adverse health outcomes; links to annoyance and sleep disruption Typical environmental levels (inconsistent)
    Solfeggio (e.g., 528 Hz) Modern New Age attributions (Puleo/Horowitz) DNA repair and restorative properties N/A (claims lack peer-reviewed validation)

    These points anchor the discussion in what’s been tested and published.

    Official Story vs. What the Data Suggests

    Institutions like the WHO maintain that infrasound is real but doesn’t reliably cause specific harms at everyday levels. Their guidelines stress reducing noise to cut annoyance and sleep issues, not some unique infrasound disease (WHO 2018).

    Acoustics experts echo this caution. Sources abound—from traffic to appliances—but lab effects don’t always replicate, and the mechanisms stay unclear.

    Defense reports, like the DTIC’s on eye resonance around 18 Hz, get cited for explaining visions. Yet they highlight the limits: small effects, tricky real-world links, nothing conclusive.

    Communities see it differently. They connect frequencies to sacred shifts or fear states, experiences passed through stories and reinforced by culture. It’s not just data; it’s felt truth.

    With AI music, the worry grows. Could algorithms bake in mood-altering sounds without users knowing? This opens ethical gaps that science hasn’t fully mapped.

    What It All Might Mean

    We can stand on this: Frequencies around 18-19 Hz show up in haunted reports and trigger effects in some experiments. Culture colors how we read them.

    But proof lags for a clear mechanism making infrasound spark hallucinations selectively. Why some feel it, others don’t—that’s the gap.

    Watch these questions: How does it work—through eyes, balance, or stress? What doses and shapes matter? Expectation’s role? And AI’s potential to scale sonic influence?

    It touches ethics in ads, public spaces, streaming. If sound sways us unseen, we need transparency rules.

    Whether the hum is physics, psychology, or a little of both, we should want to know—and to know the hands that tune it.

    Frequently Asked Questions

    Studies like Tandy & Lawrence (1998) measured an 18.9 Hz infrasound peak in a lab where staff reported cold sensations, visual anomalies, and a sensed presence. The Goldsmiths Haunt project used 18.9 Hz and 22.3 Hz, noting small increases in anomalous experiences. These provide empirical anchors, though replication varies.

    The WHO (2018) and systematic reviews find limited, inconsistent evidence for unique physiological harm from typical sub-audible infrasound. Strongest ties are to annoyance, sleep disruption, and stress, not a specific pathology. Policy focuses on reducing overall noise exposure.

    Key unknowns include mechanisms for infrasound causing apparitions in some but not others, real-world dose and configuration details, and whether AI could engineer music to steer moods without disclosure. This raises ethical stakes for transparency in production and streaming.

    Rubin and others describe sound production in spiritual terms, amplifying frequency-based explanations. This cultural framing influences how people interpret sensations, blending with occult ideas like Solfeggio frequencies, though these lack mainstream scientific support.

    Claims of restorative or DNA-healing properties for frequencies like 528 Hz stem from modern New Age sources like Puleo and Horowitz. They lack historical basis or peer-reviewed biological validation, remaining experiential rather than empirically proven.

  • Putin’s War Warning: Rhetoric or Real NATO Showdown?

    Putin’s War Warning: Rhetoric or Real NATO Showdown?

    Key Takeaways

    • Vladimir Putin’s statement on 2 December 2025, declaring Russia “ready” for war if Europe wanted one, escalated tensions amid NATO’s visible preparations like the Steadfast Defender exercise involving around 90,000 troops and forward battlegroups on the eastern flank.
    • Strongest evidence includes Reuters reporting of Putin’s remark, NATO’s public designation of Russia as the most significant direct threat, and institutional analyses from ISW and Atlantic Council highlighting Russian capability gaps despite reconstitution efforts.
    • Unresolved questions focus on whether this is genuine intent or rhetorical posturing, Russia’s capacity for sustained operations against NATO, and the origins of social media incidents—state-directed, opportunistic, or misattributed.

    A Cold Night and a War-Ready Phrase

    Picture a chill settling over Moscow on 2 December 2025, as Vladimir Putin delivers his line: Russia is “ready” for war if Europe wants one. The words hit the wires via Reuters, spreading like frost across screens in Berlin, Warsaw, and beyond. Europe woke to a split reaction—some saw it as the spark of imminent conflict, others as calculated bluff, a diplomatic shove. In our circles, those tracking security edges and anomalous events, the buzz was immediate. Telegram channels and local feeds erupted with speculation, blending fear with sharp-eyed questions about what lay beneath the surface. The mood? A tense watchfulness, like waiting for shapes to form in the fog.

    What Witnesses and Analysts Report

    From the ground up, reports have been piling in. Witnesses in the Baltic and Black Sea regions describe undersea anomalies—unexplained disturbances that some tie to sabotage. Cyber intrusions have spiked too, with local reporters noting patterns that echo state-level ops. Isolated incidents, like disrupted infrastructure, surfaced through 2024 and into 2025, shared in community forums as potential markers of bigger plays.

    Analysts point to Telegram’s role here. Open-source pieces from Euronews, SLDInfo, and MIT Technology Review detail how the platform hosts recruitment drives and influence campaigns linked to Russian interests. These aren’t just whispers; they’re documented threads pulling at the fabric of information warfare.

    Yet, context matters. Independent researchers note that Kremlin rhetoric often surges around diplomatic pivots or home-front politics. When interpreting Putin’s December 2025 comment, community voices treat these spikes as data, weighing them against firsthand accounts without rushing to judgment. It’s a mosaic—respect the pieces, question the picture.

    Timelines, Tracks, and Hard Data

    To cut through the noise, let’s anchor to what’s verifiable. Putin’s exact words came on 2 December 2025: Russia is “ready for war if Europe wants one,” as reported by Reuters. NATO’s response has been building— the Steadfast Defender exercise, announced in 2024, involved about 90,000 troops. Their posture includes eight multinational battlegroups on the eastern flank, with public statements calling Russia the most significant direct threat.

    Numbers tell part of the story. NATO’s combined active personnel sits around 3.4 million, dwarfing Russia’s 1.3 to 1.5 million, based on 2024-2025 snapshots from Statista and Visual Capitalist. Cyber fronts are active too: in July 2025, NATO publicly condemned malicious activities attributed to Russian military intelligence.

    Institutional takes from ISW and the Atlantic Council highlight Russia’s reconstitution push but flag logistics and capability gaps, with timelines shrouded in uncertainty.

    Date Event/Statement Source Why It Matters
    2024 NATO Steadfast Defender exercise announced (~90,000 troops) Reuters Signals heightened readiness and deterrence against perceived threats.
    July 2025 NATO condemns cyber activity attributed to Russian military intelligence NATO official text Highlights ongoing hybrid threats and attributes them directly.
    2 December 2025 Putin states Russia is “ready for war if Europe wants one” Reuters Escalates rhetoric, prompting questions on intent versus signaling.
    2024–2025 Russian reconstitution efforts with noted capability gaps ISW, Atlantic Council Reveals potential limits on sustaining large-scale operations.

    Official Story vs. What the Data Suggests

    Officials paint a steady picture. NATO insists it doesn’t seek confrontation but stands firm, bolstering defenses through battlegroups and exercises while labeling Russia the top threat. Government responses varied in the press—Reuters and the Guardian captured some dismissing Putin’s words as bluff, others pushing for more Ukraine aid and vigilance.

    Data backs parts of this: hard metrics on troop numbers and exercises support the deterrence claim. But analysts from ISW and the Atlantic Council add layers, noting Russia’s rebuild faces real hurdles in logistics and organization—timelines aren’t clear-cut.

    Community takes diverge. Some channels read the rhetoric as a live wire, a true threat signal. Others see it as domestic theater or bargaining chip, shaped by past patterns. Where officials downplay, these interpretations spotlight gaps—speculation fills them, but evidence sets the bounds. It’s a push-pull: trust the anchors, probe the shadows.

    What It All Might Mean

    Boil it down: Putin’s 2 December 2025 statement stands as a verifiable flashpoint, matched by NATO’s exercises, battlegroups, and documented cyber ops tied to influence campaigns. These are the solid threads.

    Questions linger. Is this intent or just words? Can Russia sustain multi-front pushes given logistics strains? What’s the line for NATO involvement? And how many of those social media incidents trace back to state actors versus lone wolves?

    Watch these signs: reserve mobilization orders, jumps in rail and transport activity, shifts in ammunition stockpiles, forward unit deployments, intelligence leaks, cyber attack patterns, and confirmed sightings of troop movements. Track them closely—they could separate bluster from buildup.

    This matters deeply. Misread rhetoric as action, and Europe faces needless panic; dismiss it, and preparations falter. For NATO, it’s about alliance strength; for eastern flank civilians, it’s daily reality. And for us tracking anomalies, it’s sorting signal from noise in a high-stakes game.

    Frequently Asked Questions

    Yes, on 2 December 2025, Vladimir Putin publicly stated that Russia was “ready” for war if Europe wanted one, as reported by Reuters. This remark amplified quickly across media, sparking debates on whether it was a genuine threat or rhetorical signaling.

    NATO’s actions include the Steadfast Defender exercise with about 90,000 troops announced in 2024, and eight multinational battlegroups on the eastern flank. They have publicly called Russia the most significant direct threat and condemned cyber activities attributed to Russian military intelligence in July 2025.

    Reports of cyber intrusions, undersea anomalies, and sabotage-style events have surfaced in 2024–2025, with some tied to Russian interests via platforms like Telegram. However, open questions remain about which are state-directed versus opportunistic or misattributed, as noted by analysts.

    Responses were mixed: some officials labeled it as rhetoric or bluff, while others called for increased vigilance and support for Ukraine, according to coverage in Reuters and the Guardian. NATO maintained it does not seek confrontation but has strengthened defenses.

    Monitor reserve mobilization notices, spikes in rail and transport logistics, changes in stockpiles, unit deployments, intelligence leaks, cyber patterns, and verified troop movements. These could indicate if rhetoric is shifting toward action.

  • Raechel’s Eyes: Inside the Hybrid Roommate Claim

    Raechel’s Eyes: Inside the Hybrid Roommate Claim

    Key Takeaways

    • Central claim: a college student was matched with a peculiar roommate (sunglasses indoors, robotic speech); the student’s mother touched the roommate and described the skin as cold and spongy, a detail recounted in the small-press book Raechel’s Eyes (Helen Littrell with Jean Bilodeaux).
    • Verifiable context: official U.S. activity on UAP has increased public interest—ODNI’s June 25, 2021 Preliminary Assessment (144 observations) and DoD’s creation of AARO (July 2022) signal institutional attention to anomalous phenomena, though not to hybridization programs.
    • Open problem: there are no publicly available, declassified government records or peer-reviewed biomedical analyses that authenticate a named, documented human-alien hybrid program; much of the hybrid narrative corpus exists in experiencer testimony, books, and community reports.

    The Girl Who Wore Sunglasses Indoors

    The apartment was small, shared by two college students scraping by on tight budgets. One, Marisa, needed affordable housing amid financial pressures. Her new roommate, Raechel, showed up with habits that set off quiet alarms. Sunglasses stayed on inside, even in dim light. Speech came out measured, almost scripted—precise, robotic, like lines from a manual.

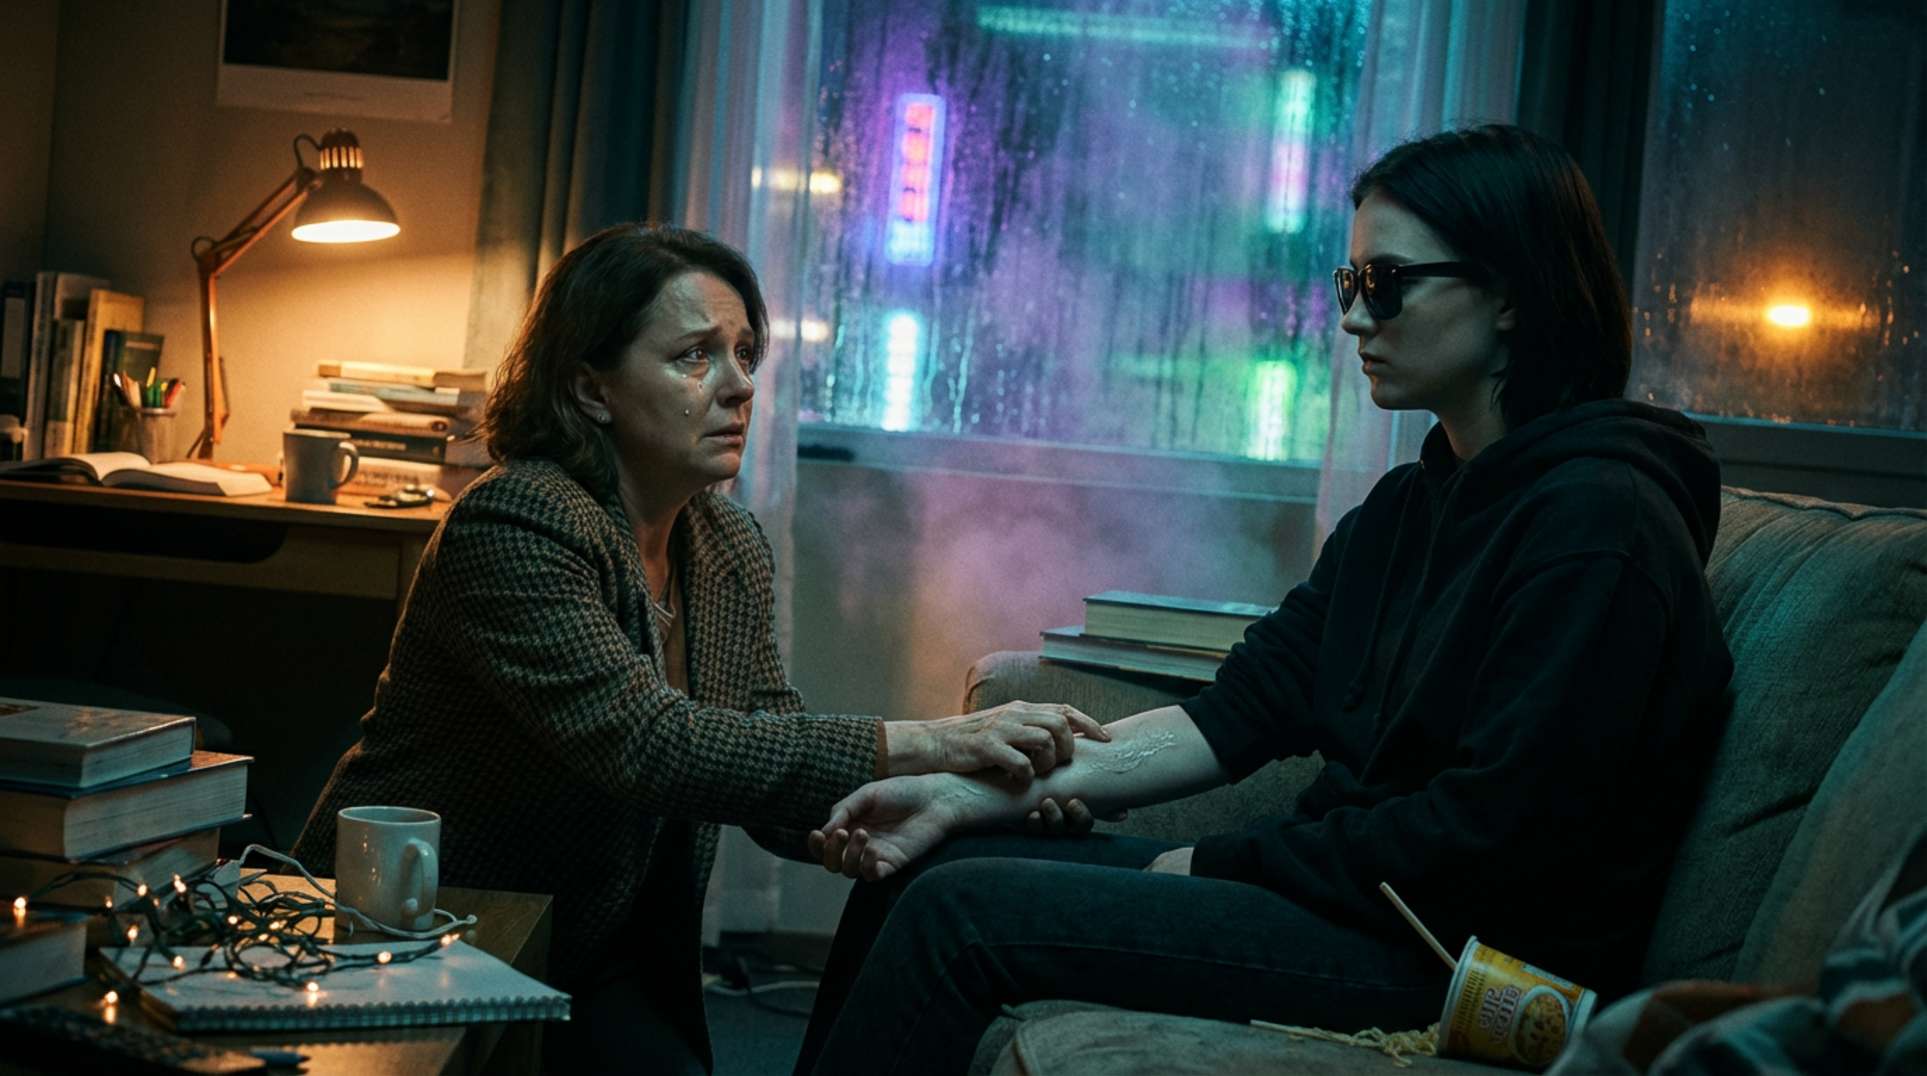
    Things escalated when Marisa’s mother visited. A casual touch on Raechel’s arm changed everything. The skin felt wrong: cold, spongy, like raw mushrooms left out too long. As detailed in Raechel’s Eyes, that moment shattered the normalcy of shared living, turning discomfort into outright suspicion. What started as odd quirks in a cramped space ballooned into a family crisis, with questions piling up fast.

    What Witnesses and Researchers Report

    Accounts like this one draw from personal experiences, shared within communities that track these patterns. In Raechel’s Eyes, the narrative describes the roommate’s sunglasses, robotic speech, and that unsettling skin texture felt by the mother. The book ties it to a supposed ‘Humanization’ or hybrid program, based on the family’s recollections.

    Across the experiencer community, similar motifs surface repeatedly. Staged introductions, clinical settings, military oversight, hypnotic regression sessions, and physical anomalies—like odd skin, eyes, or missing records—appear in reports cataloged by groups like MUFON and summarized in resources such as Hangar1 episodes. Investigators in these networks compile first-hand abduction and hybrid stories, noting recurring elements without claiming proof.

    MUFON and NUFORC serve as key hubs, gathering and archiving these accounts from witnesses worldwide. Many rely on memory recovery techniques, including hypnosis, which introduces questions about reliability. Still, the patterns persist, demanding attention from those piecing together the bigger picture.

    Timelines, Tracks, and Hard Data

    Official documents provide a foundation, even as gaps highlight what’s missing. The ODNI’s Preliminary Assessment on Unidentified Aerial Phenomena, released June 25, 2021, covered reports from November 2004 to March 2021, summarizing 144 observations, mostly from military sources.

    In July 2022, the Department of Defense established the All-domain Anomaly Resolution Office (AARO) to coordinate UAP efforts. By August 30, 2022, AARO noted around 510 reports in its historical record.

    Raechel’s Eyes, by Helen Littrell with Jean Bilodeaux, stands as the primary source for this roommate account, framing it within a hybrid program narrative. Yet no declassified records from DoD, ODNI, DARPA, NIH, or CDC confirm such a program, including budgets or medical details.

    Key Data Point Details
    ODNI Preliminary Assessment June 25, 2021; 144 observations (Nov 2004–Mar 2021)
    AARO Establishment July 2022 (DoD memo)
    AARO Reports ~510 as of August 30, 2022
    Raechel’s Eyes Book by Helen Littrell with Jean Bilodeaux; documents roommate claim and ‘Humanization’ narrative
    Confirmed Government Program None publicly available for human-alien hybrids

    To strengthen quotes, excerpts from Raechel’s Eyes—via OCR if needed—could verify the exact tactile description.

    Official Story vs. Community Interpretations

    Government agencies frame UAP as a matter of data collection, flight safety, and security. The 2021 ODNI report avoided extraterrestrial attributions, leaving many cases unexplained but tied to practical concerns. AARO, since 2022, focuses on identification and coordination, often resolving incidents to everyday causes, with no public confirmation of alien origins.

    In contrast, experiencer communities see hybrid programs as tangible operations, sometimes linked to human agencies. These views spread through books, conferences, and networks like MUFON or Hangar1, where witnesses describe structured integrations of hybrids into society.

    The divide is clear: official records track aerial anomalies but lack biomedical evidence for hybrids, such as medical records or forensic tests. This gap leaves community claims strong on testimony but short on verifiable chains of proof.

    What It All Might Mean

    The core incident—the mother’s touch revealing cold, spongy skin—comes from Raechel’s Eyes. Meanwhile, documented UAP activity via ODNI in 2021 and AARO in 2022 shows real institutional focus, but nothing confirms a hybrid program.

    Questions linger: Do hidden memos or budgets back a ‘Humanization’ project? Are there medical records for alleged hybrids? How reliable are hypnotic regressions in these stories?

    These claims touch on oversight and ethics if covert programs exist, or they highlight how people process anomalies if not. For next steps, pursue FOIA requests on program names, secure excerpts from Raechel’s Eyes, interview authors and witnesses, check MUFON/NUFORC for parallels, and consult experts on the described skin traits. Documents support parts of this; testimony fills the rest. Weigh it for yourself—mystery remains.

    Frequently Asked Questions

    A college student shared an apartment with Raechel, who wore sunglasses indoors and spoke robotically. The student’s mother touched Raechel’s arm, feeling skin that was cold and spongy like mushrooms, as detailed in Raechel’s Eyes. This sparked suspicions of a hybrid program.

    No publicly available declassified government records or peer-reviewed analyses confirm such programs. Official focus, like ODNI’s 2021 report and AARO’s work, addresses UAP as safety and security issues without endorsing hybrid claims. Community narratives rely on testimony and books.

    Agencies like ODNI and AARO treat UAP as data and security matters, often explaining them mundanely without alien attributions. Experiencer communities interpret hybrids as real programs, shared through networks like MUFON, highlighting patterns in testimony that lack official biomedical backing.

    Pursue FOIA requests for program details, obtain excerpts from Raechel’s Eyes, interview authors and witnesses, query MUFON/NUFORC for similar cases, and consult medical experts on the skin description. This builds on documented UAP activity while addressing testimony gaps.

    It connects personal experiences to broader patterns in hybrid narratives, amid rising official UAP attention. If true, it raises ethical and oversight issues; if not, it shows how communities interpret anomalies. Readers can assess the evidence themselves.